
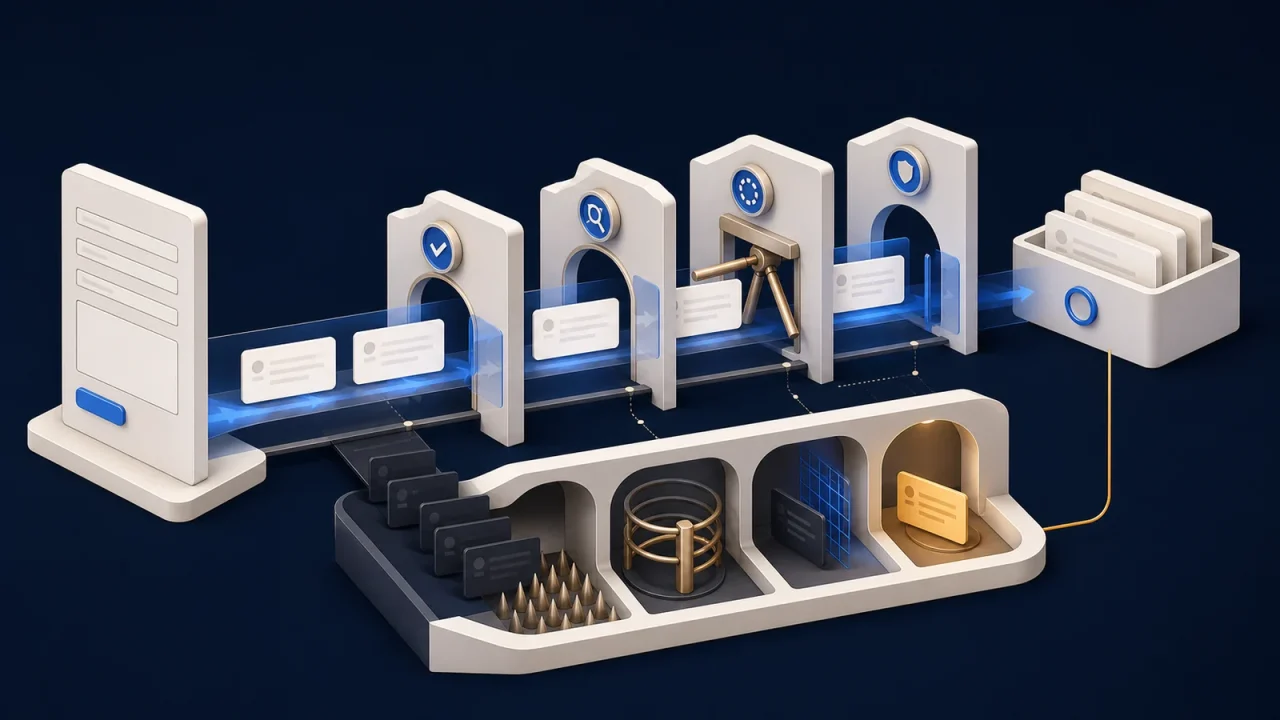
Effective website form spam protection layers several server-enforced controls and adds friction only when a submission looks suspicious. A CAPTCHA widget by itself is not a complete implementation, and forcing every legitimate visitor through a difficult challenge can reduce the inquiries the form exists to create.
The goal is not to prove every visitor is human. It is to keep abusive submissions from becoming trusted business records.
A practical design combines input validation, hidden bot traps, timing and rate signals, replay protection, selective challenges, monitoring, and a review path. The right combination depends on the value of the form and the cost of blocking a real customer.
Website form spam protection starts on the server
Anything enforced only in the browser can be bypassed by sending requests directly to the form endpoint. Validate required fields, allowed lengths, formats, file types, and anti-bot evidence again on the server. Keep secrets out of page source and do not trust a hidden field simply because the normal interface does not show it.
This applies to challenge products too. Cloudflare’s Turnstile documentation says server-side validation is mandatory because client tokens can be invalid, expired, forged, or replayed. Its tokens are provider-specifically described as single-use and valid for five minutes.
Google’s reCAPTCHA verification documentation likewise requires the backend to verify a response token and documents its own token lifetime and single-use restrictions. These products differ, but the shared implementation rule is clear: the server decides whether the submission is accepted.
Use low-friction signals before a challenge
A honeypot is a field that normal users should leave empty but simplistic form-filling bots may complete. A timing check can flag a long form submitted almost instantly. Duplicate content, impossible field combinations, known disposable addresses, and repeated destination URLs can add evidence.
No single signal should be treated as universal proof. Password managers and assistive technology can interact with fields in unexpected ways. Fast submissions can be legitimate. IP addresses may represent many people behind one network. Combine signals into a policy and test it against real use.
For low-risk contact forms, suspicious submissions can enter a review queue instead of being deleted. That gives the team evidence to tune the rules without losing a valuable lead.
Rate-limit the action that creates cost
Limit repeated submissions before they generate email, create CRM records, upload files, send SMS messages, or call paid APIs. Apply limits to a useful combination of IP, session, account, form, destination, and time window rather than one identifier alone.
The standard HTTP response for rate limiting is 429 Too Many Requests, and it may include a Retry-After header. A public form may show a friendlier message, but the backend should still record the limited action and avoid performing downstream work.
Set limits from observed legitimate traffic and the cost of abuse. A support form used by one customer several times during an incident needs different rules from a newsletter form that should receive one address once.
Escalate suspicious traffic selectively
Run quiet checks first, then request a challenge or stronger verification when risk increases. A second attempt after a failed honeypot, a burst of repeated submissions, or an action with direct financial cost may justify more friction than an ordinary first-time inquiry.
The escalation must have usable success, failure, expiry, unsupported-browser, and retry states. If the challenge provider is unavailable, decide whether the form fails closed, queues the submission, or offers another contact method. That decision should reflect the form’s risk rather than being an accidental timeout behavior.
Protect accessibility and conversion
Test the entire form with keyboard navigation, screen readers, browser zoom, mobile devices, autofill, password managers, slow connections, privacy tools, and common content blockers. Keep error messages close to the affected field and explain how to recover without exposing the anti-spam rule.
Offer a legitimate alternative when the form cannot be completed, such as a clearly published phone number or email path with its own spam controls. Do not create a challenge loop that repeatedly clears entered information.
Measure completion rate and validation failure alongside spam volume. A system that blocks every bot by blocking many prospective customers is not performing well.
Keep spam out of downstream automation
Do not send an untrusted submission directly into sales automation, email sequences, ticketing, analytics conversions, or AI processing. Store its validation result, risk signals, source form, and decision before downstream systems treat it as a lead.
Use idempotency or a submission identifier so retries do not create duplicate contacts and notifications. Sanitize content before displaying it in internal tools, and scan uploads before making them available to staff.
Monitor false positives as carefully as spam
Track accepted submissions, rejected submissions, challenge requests, verification failures, rate limits, duplicates, review outcomes, and completion rate. Segment results by form and traffic source so one attacked endpoint does not cause stricter controls everywhere.
Review samples of both accepted and rejected traffic. Changes in bot behavior, campaign traffic, browsers, or form design can make yesterday’s rules inaccurate. Assign an owner to adjust controls and verify the downstream CRM and notification paths still work.
Use a practical form-protection checklist
- Validate all inputs and anti-bot evidence on the server.
- Add low-friction honeypot, timing, duplicate, and content signals.
- Rate-limit costly actions before downstream processing.
- Use single-use submission identifiers and replay controls.
- Escalate suspicious traffic instead of challenging everyone.
- Test accessible success, failure, expiry, and recovery states.
- Measure false positives, completion, spam, and review outcomes.
Protect the business process, not just the inbox
Form spam becomes expensive when it contaminates the systems and decisions behind the website. Layer quiet controls, enforce them on the server, add friction according to risk, and keep legitimate failures recoverable.
This belongs in the recurring care model described in A Website Maintenance Plan Should Protect the Operating System. If public forms are creating noise or blocking real inquiries, Eckman Design can help review the full form and automation path.
Discussion
0 Comments